Category: Uncategorized

  • Is my Mac laptop sharing my location?

    how is this ZIP code being sent?

    Is my Mac laptop using cell tower information to calculate and transmit my location to third parties? I believe the answer is yes.

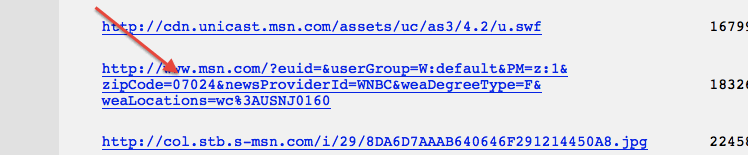
    Here is my evidence. I cleared recent history from Firefox, selected private browsing, then typed “Msn.com” into my browser. Then I looked at what was stored in my cache (using about:cache), and I found this entry (see above).

    This entry is a message from my browser to msn.com with whatever data can be passed along. Notice the “euid” field is empty. That is good, I am using private browsing. Then notice it is passing back my zip code as 07024, and my local news provider as WNBC. Is this coming from my IP address?

    The answer is no, it is coming from cell tower location information. How do I know this comes from cell tower rather than my IP address?

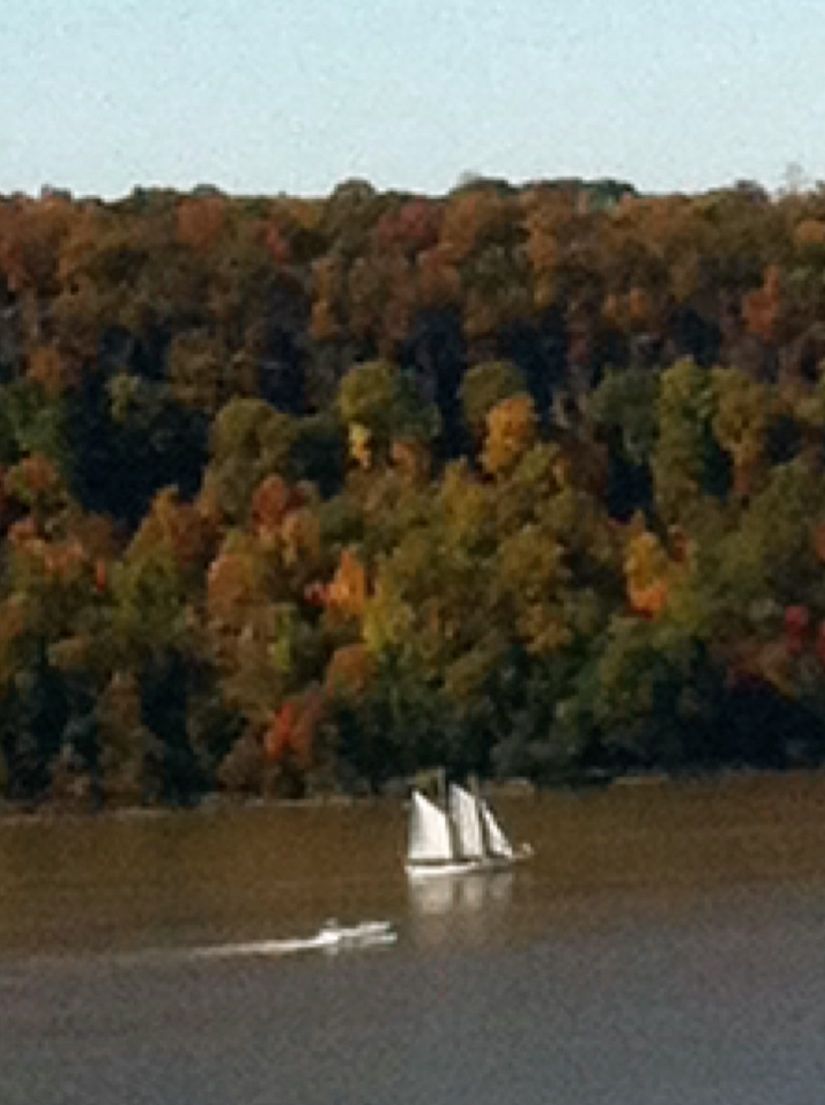
    The zip code transmitted is  07024 (Fort Lee, NJ). However I live right across the river is Washington Heights, upper Manhattan (below is the view of New Jersey from Washington Heights).  Often 911 calls via cell phone from my neighborhood get routed to New Jersey by mistake due to our close proximity to NJ cell towers. So my zip code is not coming from my IP address, which comes from Time Warner, hence it should be a NYC zip code, not a NJ zip code. It seems to be coming from cell tower triangulation, being collected and passed along by my Mac laptop :(

    View of New Jersey from Washington Heights
  • One person’s trash is another person’s… medical record?

    Joe Hall here.

    An intriguing story flew past my Twitter stream, that begins:

    “MINNEAPOLIS (WCCO) — Detailed medical information discovered on the back of a first-grader’s school drawing sent Minneapolis school officials scrambling.

    Jennifer Kane was tidying her dining room when she found the drawing by her daughter, Keely, who goes to Hale Elementary School. On the back of the paper was the name, birth date and detailed medical information for a 24-year-old St. Paul woman named Paula White.” –(“Recycled Medical Records Used As Scrap Paper At School”)

    Long story, short: Ms. White’s records that she voluntarily gave to a law firm representing her after a car accident were donated by a paralegal to Ms. Kane’s daughter’s elementary school.  These records, and those of presumably many others, were found by school officials after being used as scrap paper and have since been secured, probably waiting disposal (or, cynically, placed in escrow until the new team of lawyers Ms. White might hire to sue her old lawyers get a chance to look at them!).

    Ms. White expresses concerns that we see often in cases of privacy breaches, especially medical breaches: “It’s got my account number, my birth date, my job … I’m outraged. I am embarrassed. I don’t want anyone to know my personal information.”

    What recourse does she have?  Likely, the only thing she can do is hire another law firm to sue the first law firm; that is, there’s no federal health privacy issue here. Because the law firm is not a “covered entity” under the federal law and accompanying regulations known as the Health Insurance Portability and Accountability Act (HIPAA), the responsible enforcement agency, the department of Health and Human Services, can’t seek corrective action.  In fact, you may be surprised how little HIPAA and HHS can do in situations like these. Our friends at the World Privacy Forum keep a very useful FAQ about HIPAA and also point out how medical identity theft, where people use medical information about others to obtain services or make fraudulent claims, is on the rise and an increasing concern for patients.

    What can you do? Be vigilant, as always. Make sure you monitor and understand your health insurance claims information and that you let your health care providers know if you suspect funny business. Of course, if a law firm you hire screws up this bad, find a new one and teach the old one a lesson with a good old fashioned legal malpractice lawsuit.

    Updated on 11/22 to make clear that Ms. White can sue the original law firm for malpractice. –JLH

  • Orin Kerr on United States v. Jones

    Orin Kerr ponders oral arguments in United States v. Jones (reposted from The Volokh Conspiracy):

    I was at the Supreme Court this morning for the oral argument in United States v. Jones, the GPS case. In this post, I want to blog my reactions to the argument: I’m going to update the post as I go, so general readers can get the important stuff first at the top and then general readers can get the rest down the page:

    (more…)

  • EPIC files FTC complaint against Verizon

    As a follow-up to Helen’s post about Verizon’s new privacy practices, EPIC has filed an FTC complaint alleging that the move amounts to an unlawful trade practice.

  • Android orphans and the update problem for smartphone security and privacy

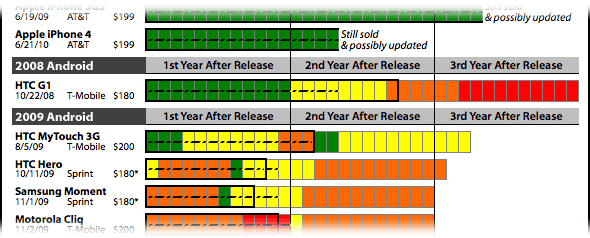
    Michael Degusta has a wonderful blog post up about the history of missing software updates for Android smartphones, compared to Apple’s iPhone. A sample:

    Android Orphans

    In this chart, green blocks represent periods when a phone ran the most up-to-date major version of its operating system, while yellow, orange, and red blocks represent periods where a phone could only run increasingly out-of-date major versions. See Michael’s post for the full chart and some great analysis.

    Two factors combine to make the lack of updates a significant problem. First, in the United States at least, most phones are sold on two-year contracts, so a lack of updates means they will almost certainly be used well after their OS is no longer the current version. Second, since smartphones are constantly connected to the cell-phone network and the Internet, they present an attractive and vulnerable target for malware authors when security vulnerabilities are discovered. If updates can’t be applied to many of the smartphones in use, then the potential harm from a security problem expands greatly. Indeed, the many Android privacy and security problems show the potential severity of the issue.

    So what is to be done? It’s understandable why, in the fast-moving and competitive market for Andoid smartphones, makers don’t want to spend money supporting devices they’re no longer selling. Yet if two-year contracts are the standard, it may not be unreasonable for users to expect makers to support a device for at least two years after they stop selling it. With the FTC’s recent reemphasis on trade practices that are “unfair” but not necessarily “deceptive” (a subject worthy of a post of its own), it will be interesting to see if the agency has anything to say about the Android orphan problem.

  • TPM – Feds To Monitor Google’s Privacy Practices For Next 20 Years

    From TalkingPointsMemo:

    “Feds To Monitor Google’s Privacy Practices For Next 20 Years

    Sarah Lai Stirland October 24, 2011, 4:10 PM 942 5

    The U.S. Federal Trade Commission on Monday finalized a landmark settlement with Google in which the company has agreed to be audited for its privacy practices for the next 20 years.

    The commission has said that this is the first time that it has required any company to formally implement a comprehensive privacy program to protect individuals’ personal information.

    The FTC commissioners voted to approve the settlement 4-0, after the period for public comment ended. The proposed settlement was announced in March.

    The FTC case was prompted by the now-defunct Google Buzz social networking service. Google tried to tack Buzz onto Gmail users’ e-mail accounts, enabling them to provide status updates and to share photos and videos, but it created an uproar when it made users’ Gmail contacts public by default.

    The commission charged that Google engaged in unfair and deceptive practices in 2010 when it launched Google Buzz by leading users of its Gmail system to believe that they could easily opt-out of the social network. The controls that would enable them to do that were ineffective, the FTC charged at the time.

    Also the tools that Google created to enable users to limit the sharing of users’ personal information were confusing and difficult to find, the agency alleged.

    In its complaint, the FTC said that Google had enrolled some Gmail users in Google Buzz even after the users had clicked on a tab to decline to use the service, and that the identities of people that Gmail account holders most frequently communicated with were made public by default. Worse, when users tried to get out of the service, they weren’t fully removed.

    In a press statement on the settlement, the FTC noted, “In response to the Buzz launch, Google received thousands of complaints from consumers who were concerned about public disclosure of their email contacts which included, in some cases, ex-spouses, patients, students, employers, or competitors.”

    Google made changes to respond to those complaints, but the FTC went after the company because Google had violated its own privacy policy by using its users’ personal information in a way that they had not consented to even though Google had said they would ask for permission first.

    The commission had also charged that the way that Google had gone about representing the way its users’ personal information would be displayed was deceptive. Users didn’t know, for example, that their most frequently e-mailed contacts would be made public by default.

    The FTC’s settlement with Google requires the company to inform and obtain its users’ consent before it shares any of their information with third parties, and subjects the company to 20 years of privacy audits every two years by an independent third party monitoring service. The audits are meant to ensure that Google is living up to its promises about what it is doing with its users’ personal information. The company is also required to implement a comprehensive “privacy program.”

    Google recently killed its disasterous Google Buzz project, which had been long abandoned in favor of its Google+ social network, which has met with general praise for the way it enables users to control how they share information on a fine-grain level.

    In an e-mail to TPM, Google’s Senior Manager of Global Communications Chris Gaither said that Google has completely revamped the way it approaches privacy.

    Instead of being an afterthought, privacy is a concept that’s considered during the design of new products.

    “We’ve strengthened many of our internal privacy and security controls over the past year,” he said. “For example, in October we appointed longtime Google engineer Alma Whitten to director of privacy across product management and engineering.”

    In addition, Gaither says, “We’ve increased privacy training for all our employees. We’ve tightened our compliance controls for those who deal with sensitive data. And last fall, we added a new process to our existing privacy review system requiring every engineering project leader to maintain a Privacy Design Document for each initiative they are working on. This document records how user data is handled and is subject to regular review.”

    Like other technology companies, Google had come increasing fire both here in the United States and especially in Europe over privacy issues.

    Last May, Google inadvertently collected data from private WiFi networks when its Street View cars drove by. Google has since been investigated by the regulatory authorities in Europe over the incident.”
  • New privacy study shows top-ranked sites selling user information

    The WSJ just blogged about a recent internet privacy study implicating several high-traffic sites of selling user information to third party SEO companies.  Sites include OKCupid!, RottenTomatoes, and yes, the Wall Street Journal herself.

    Nothing new here, but note WSJ’s clever loophole: they don’t sell users’ email addresses; instead, they sell email addresses used in failed login attempts, meaning that potential privacy issues are squelched because the addresses they sell are technically not attached to any users.

  • CSCW Workshop: Reconciling Privacy with Social Media

    CSCW Workshop: Reconciling Privacy with Social Media

    February 12, 2012

    Full Details: http://phitlab.host22.com/cscw2012privacyworkshop.html

    Call for Participation

    Much research on privacy in social media has focused on limiting personal information disclosure, increasing control, and perpetuating social withdrawal. Therefore, privacy goals are often characterized as diametrically opposed to goals of sharing and connecting via social media. However, privacy can also be characterized as a broader process where individuals and groups coordinate social interaction with others. In this broader conceptualization, privacy behavior moves beyond binary decisions to withhold or disclose and becomes an interactional process that involves the cooperation of others in the relationship. The goal of this workshop is to explore privacy in broader contexts and to understand its relationship to the benefits of social media and the support of online cooperative relationships.

    The workshop will focus on two main themes: Focusing on the benefits and outcomes of interactional privacy behaviors in social media environments, and emphasizing design and evaluation solutions for bringing such benefits to fruition.

    We invite potential workshop participants to submit 2-4 page position papers that describe research related to the workshop themes. The deadline for submission is November 25.

    Please see the workshop website at http://phitlab.host22.com/cscw2012privacyworkshop.html for more information.

    Workshop Co-Organizers:

    Heather Richter Lipford, University of North Carolina at Charlotte

    Pamela Wisniewski, University of North Carolina at Charlotte

    Cliff Lampe, University of Michigan

    Lorraine Kisselburgh, Purdue University

    Kelly Caine, Indiana University Bloomington

    Program Committee:

    Coye Cheshire, University of California Berkeley

    Catherine Dwyer, Pace University

    Woodrow Hartzog, Samford University

    Adam Joinson, University of Bath

    Jen King, University of California Berkeley

    Airi Lampinen, Helsinki Institute for Information Technology HIIT & University of Helsinki

    Deirdre Mulligan, University of California Berkeley

    Fred Stutzman, Carnegie Mellon University

    Janice Tsai, Microsoft

    Michael Zimmer, University of Wisconsin-Milwaukee

  • Twitter, FTC vs. Frostwire, CA and cell phones

    from Joe Lorenzo Hall

    Twitter starts wrapping all hyperlinks through t.co
    http://venturebeat.com/2011/10/10/twitter-url-wrapping/

    “Twitter has various reason for forcing all hyperlinks through t.co.
    It eliminates the security risk posed by third-party short link
    services (like Tinyurl and bit.ly) that don’t allow the company to
    screen for malicious links. But more importantly, t.co URL wrapping is
    central to Twitter’s new web traffic analytics service unveiled in
    September.”

    —-

    FTC vs. Frostwire (filed: 10/7/2011)

    http://www.ftc.gov/os/caselist/1123041/111011frostwirecmpt.pdf

    Interesting because as opposed to much of FTC action lately in this
    space, the violations not only include deceptive practices but *also*
    unfair practices, indicating that not only was Frostwire not
    forthcoming with how their filesharing application works, but also
    that they caused substantial harm to consumers (by default sharing
    private files — “pictures, videos, unprotected applications,
    documents, music and audio files, and ringtones.” — publicly, and
    making it difficult for users to do otherwise).

    —-

    CA Gov. vetos bill that would require warrant to search cell phones of arrestees
    http://www.wired.com/threatlevel/2011/10/warrantless-phone-searches/